
Data classification & labels
A clear classification for sensitive information. Together, we decide when markings, access restrictions or encryption are needed.
You receiveA label design that fits your organisation
Take control of sensitive information.
Your data deserves protection that fits your organisation. IR-IT turns your information policies into clear labels, tested DLP rules and a configuration your team can manage.

Our expertise
We identify which information needs protection and configure Microsoft Purview accordingly, with attention to security and the everyday work of your people.
A clear classification for sensitive information. Together, we decide when markings, access restrictions or encryption are needed.
DLP policies for the agreed locations, such as Exchange, SharePoint, OneDrive, Teams or devices. We review signals and test rules before rollout.
From design to a working configuration. Your operations team receives documentation and guidance on policies, settings and design decisions.
Product information: Microsoft Purview Information Protection & Data Loss Prevention.
The approach
Which data, risks and ways of working matter? We map your starting point and licences.
We create a label design and DLP plan, with clear decisions on scope and exceptions.
We configure the agreed components, test with a pilot group and roll out after evaluation.
Your team receives documentation, operational guidance and an overview of the next steps.
Your dedicated contact
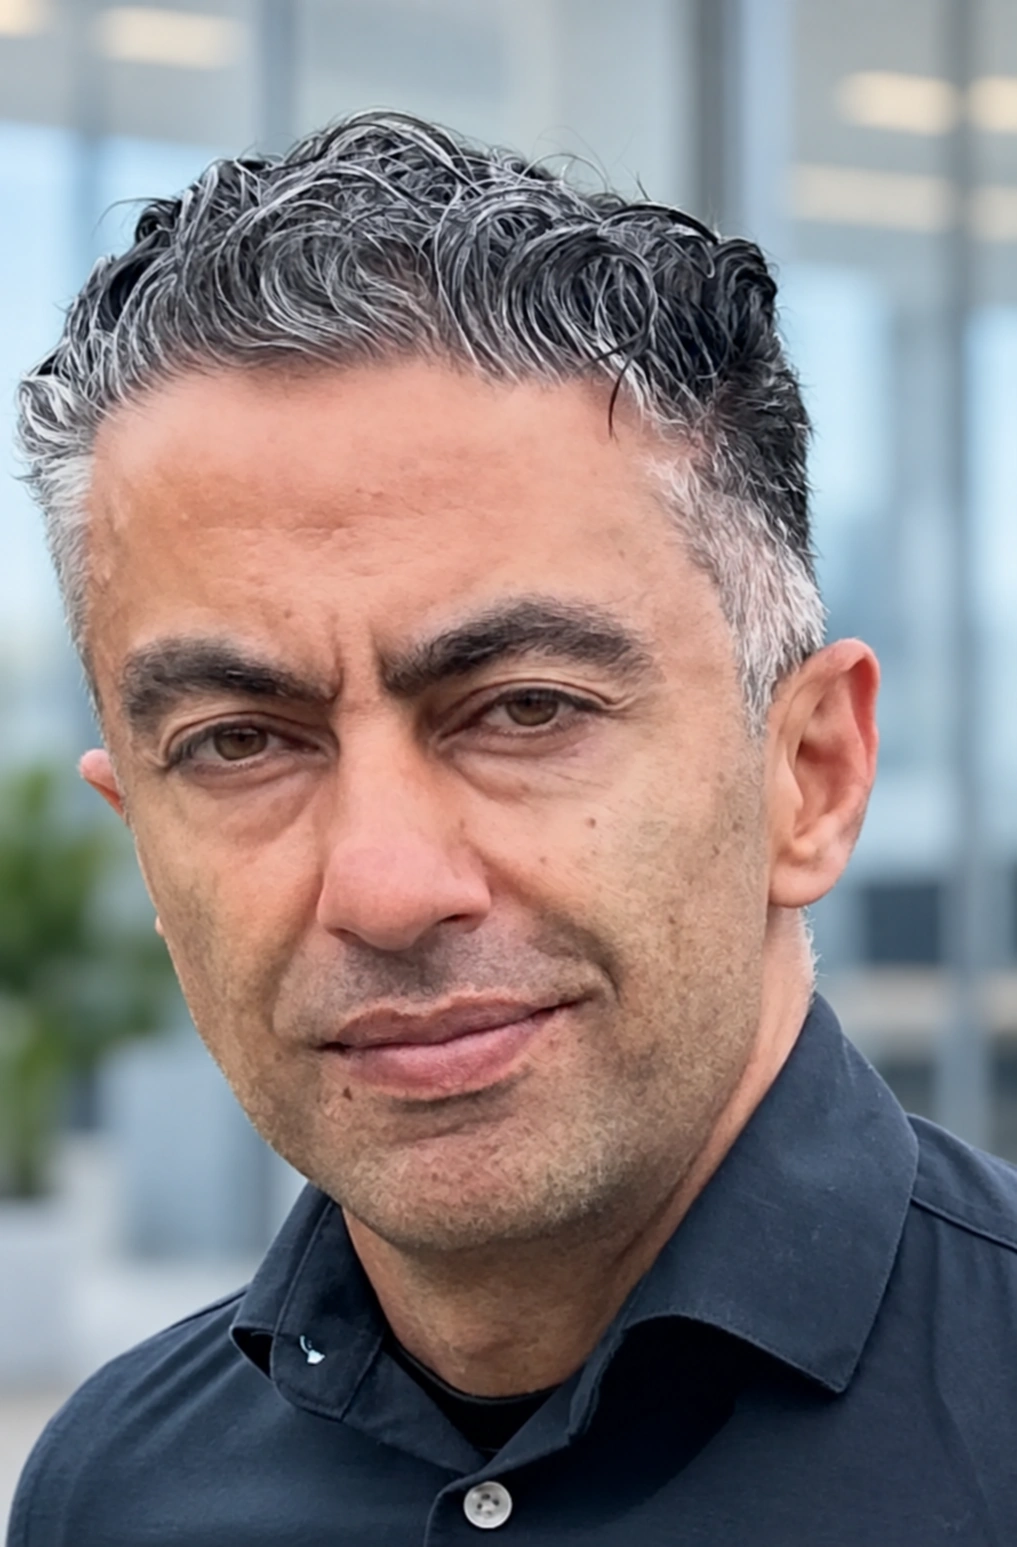
The specialist who advises you also handles the technical implementation. With more than 18 years of IT experience and assignments at major organisations in financial services, government and professional services.
Frequently asked questions
You receive a tested configuration for the agreed components, with documentation of policies, exceptions and decisions. During handover, your team receives guidance on administration and next steps.
For an initial implementation, uncertainty about sensitivity labels, or DLP rules that flag too much or too little. Support can also focus on a specific part of your existing environment.
Sensitivity labels indicate how confidential information is. Depending on their settings, they can also encrypt a document or email or add a visible marking. A label without protection settings does not automatically restrict sharing.
Data Loss Prevention (DLP) checks whether information is being used or shared in line with your policies. For example, a rule can warn or block when sensitive data is shared externally. DLP can assess the content and, where supported, the sensitivity label. Start by deciding which information may be shared with whom. Read Microsoft's guidance on sensitivity labels and DLP.
Yes. Simulation mode evaluates a DLP policy without enforcing that policy's blocking actions. Other security rules that are already active still apply. The simulation shows which information is detected and which alerts are generated.
A useful pilot includes situations that should be detected and normal work that should be allowed. Review the results with employees, adjust detection criteria and exceptions, and agree who will handle alerts. This helps establish when enforcement can safely begin. Microsoft explains this approach in its guidance on DLP simulation mode.
For advanced capabilities, such as Endpoint DLP and automatic sensitivity labelling, you need Microsoft 365 E5 or an equivalent combination of licences as a minimum. Microsoft 365 E3 may be sufficient for some basic capabilities. We check in advance that your licences cover all the features you need.
Purview focuses here on sensitive information and data loss. Defender adds protection and threat detection for devices, identities and email, among other areas. They can be implemented separately or together. Learn more about the Microsoft Defender specialist.
Your next step
Tell us where your organisation stands and what you want to achieve. Discuss your needs directly with Parviz.
Book an introduction