
Endpoint & Office 365
We onboard the agreed devices and align security policies. For email and collaboration, we configure the selected protection against malicious messages, links and attachments.
You receiveProtection for devices and email
Security that works together.
Devices, identities, email and cloud apps: turn separate components into a coordinated defence. IR-IT configures Microsoft Defender, validates its operation and hands it over to your team.

Our expertise
Effective security takes more than individual settings. We align the selected Defender components so your team can investigate threats and respond with purpose.
We onboard the agreed devices and align security policies. For email and collaboration, we configure the selected protection against malicious messages, links and attachments.
Identity threat detection and visibility into cloud apps. We assess which connections are needed and align the configuration with your existing environment.
We bring available signals together and validate detection and response settings, with attention to roles, alerts and the way your security team works.
Product information: Microsoft Defender XDR.
The approach
We review coverage, settings, licences and risks. Together, we set the priorities.
We plan the selected Defender components, integrations, roles and exceptions.
We implement in stages, verify the onboarding of devices and services, and test alerts.
Your team receives documentation, guidance on settings and an overview of outstanding issues.
Your dedicated contact
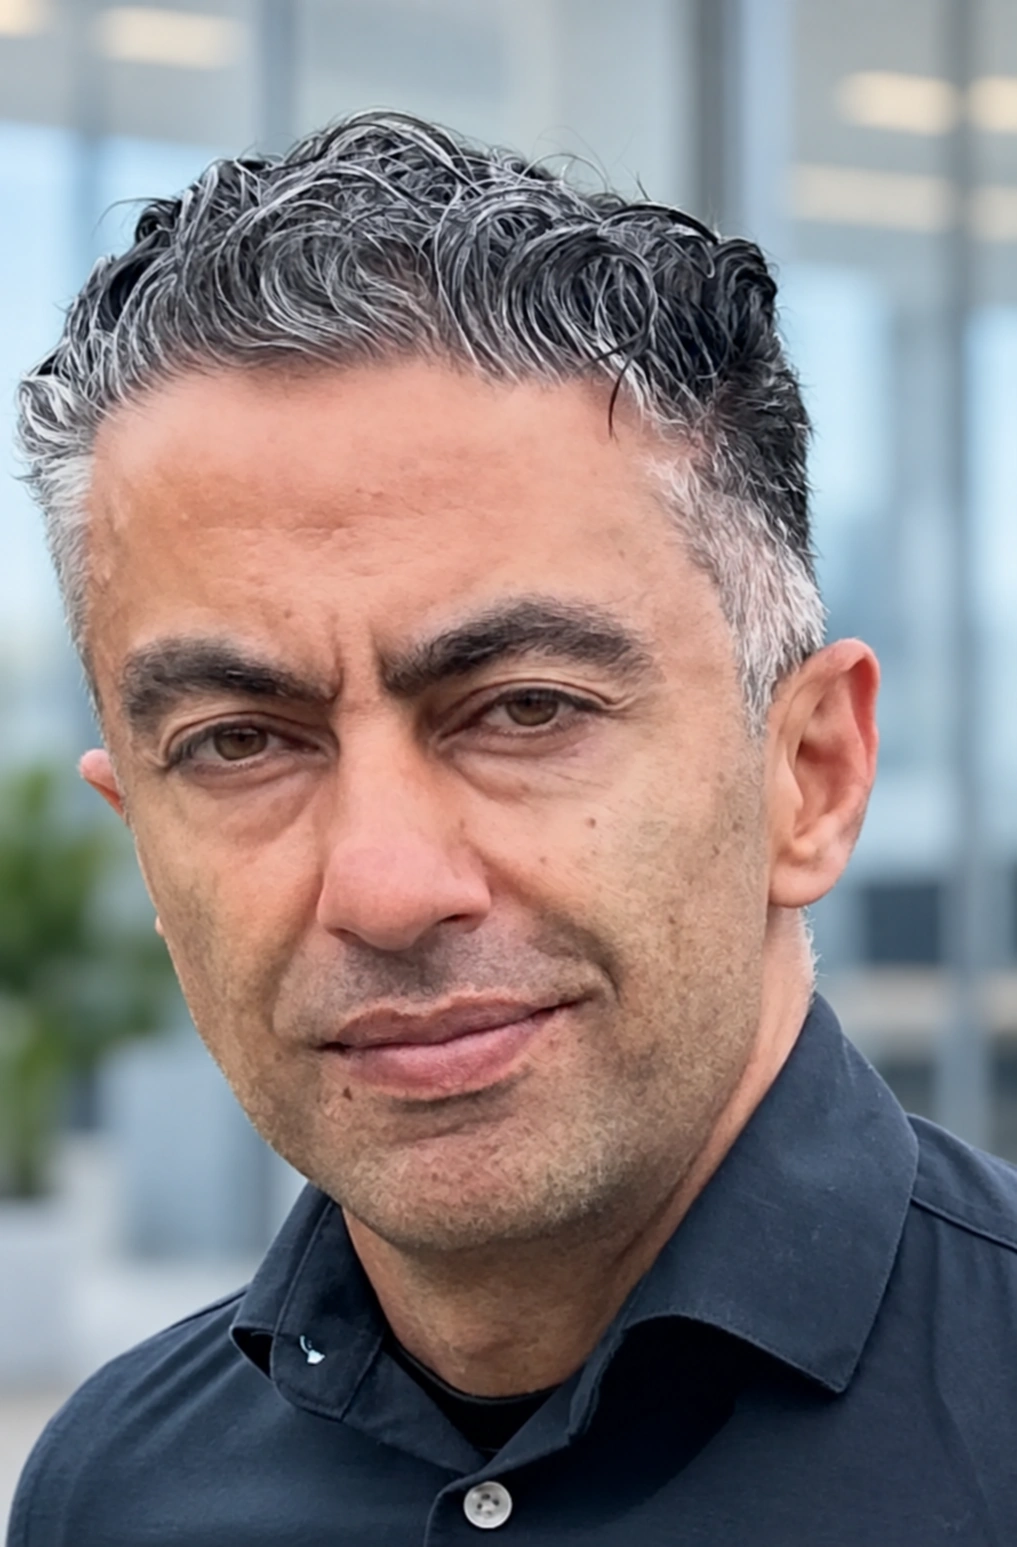
The specialist who advises you also handles the technical implementation. With more than 18 years of IT experience and assignments at major organisations in financial services, government and professional services.
Frequently asked questions
You receive a configuration for the agreed Defender components, with validated security policies and detection settings. Documentation and handover help your IT or security team assess alerts and administer the environment.
Support covers Defender for Endpoint, Defender for Office 365, Defender for Identity and Defender for Cloud Apps, integrated through Defender XDR. The exact scope depends on your environment, priorities and licences.
Yes. For example, when devices are not correctly onboarded, policies do not fit the organisation or alerts are difficult to assess. We start with the specific problem and determine the changes needed.
Defender supports protection and threat detection across your IT environment. Purview helps identify and protect sensitive information. Is your main focus classification, labels or DLP? See the Microsoft Purview specialist.
Your next step
Tell us where your organisation stands and what you want to achieve. Discuss your needs directly with Parviz.
Book an introduction